Forging a Microsoft Edge Full Chain with Logic Bugs Only
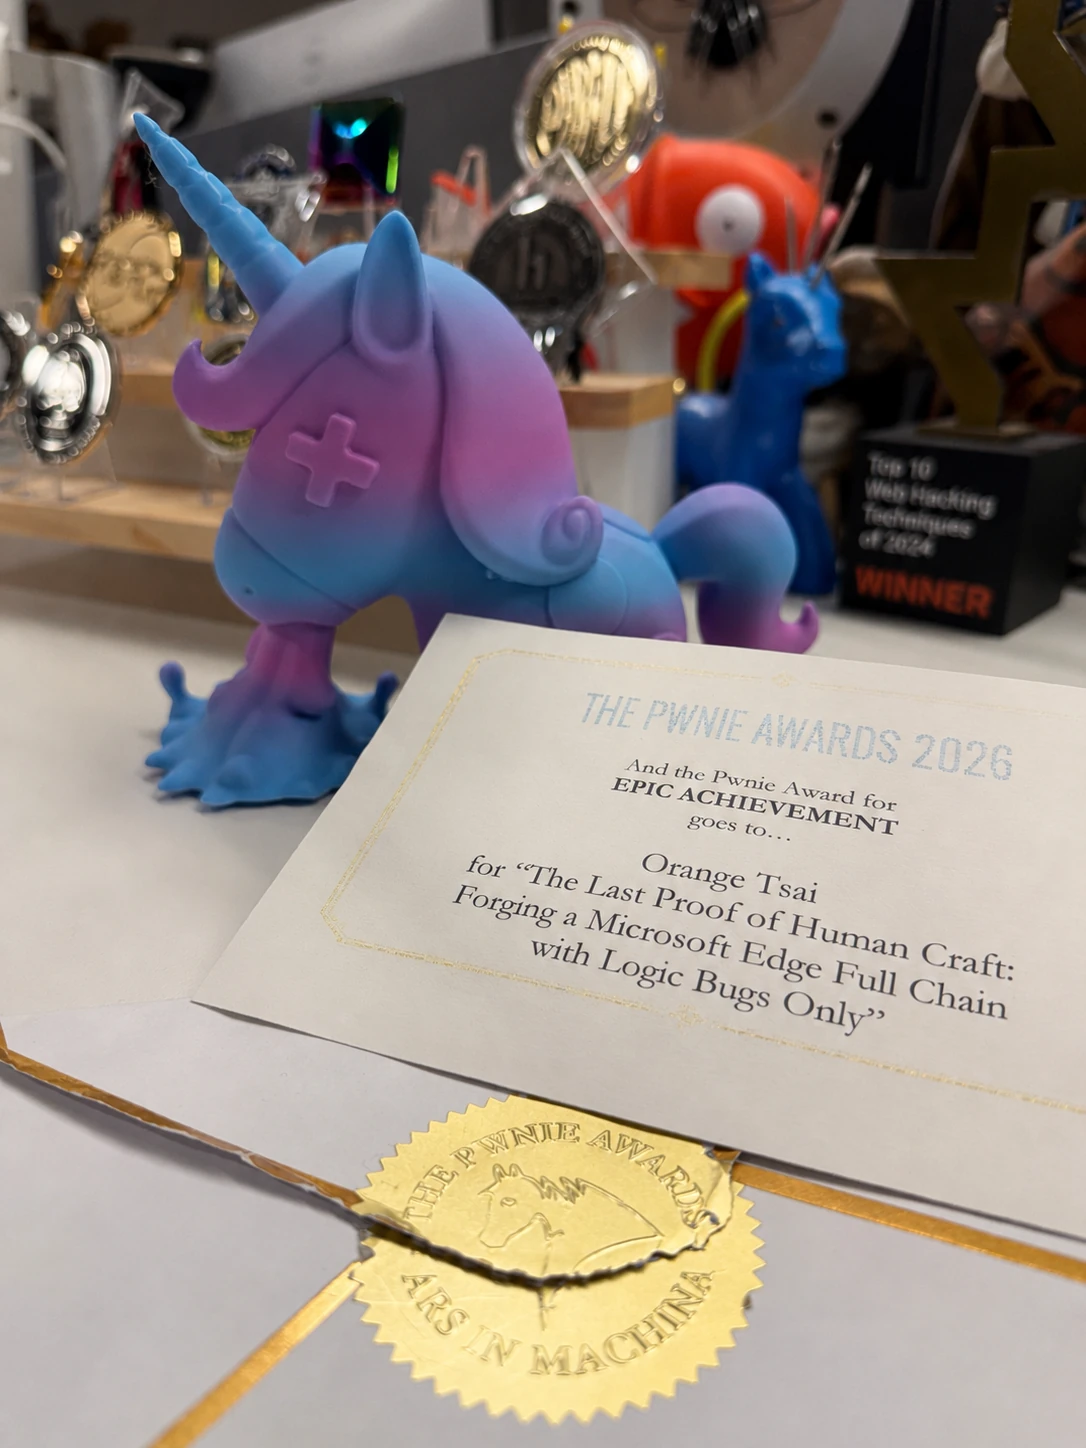
This is what I built for Pwn2Own Berlin 2026 - a completely handmade, logic-only Microsoft Edge Full Chain, with no memory corruption, and no AI at all! 🔥
Quick read
A detailed write-up of a logic-only exploit chain that achieved a Microsoft Edge sandbox escape at Pwn2Own Berlin 2026. It explains the discovered navigation-throttle bug, how it leads to a UXSS primitive, and the chaining process used to weaponize it.
- Explains EdgeCAGuidanceNavigationThrottle and its origin-check bypass
- Shows how browser-initiated navigations can produce a sourceless UXSS
- Describes chaining multiple logic bugs to achieve sandbox escape
Reactions
No reactions yet. Record a short about this link and it shows up here, in Reels and in the community feed.
Is blog.orange.tw your site? Sign in to verify it and get a Verified badge, full stats and a link-back badge.
A closer look at Forging a Microsoft Edge Full Chain with Logic Bugs Only
What this write-up is about
This post documents a handcrafted, logic-only Microsoft Edge full chain that was built for Pwn2Own Berlin 2026. The author describes chaining logic bugs (no memory corruption) to escape Edge’s sandbox, and explains parts of the bug-hunting and chaining process that led to that result.
What you can read and follow on the page
The article walks through the navigation flow in Chromium and focuses on a thinly attended area called Navigation Throttles, pointing out an Edge-specific throttle named EdgeCAGuidanceNavigationThrottle used for Conditional Access (Entra ID). It explains how that throttle inspects an email parameter and can cancel and relaunch navigations with an attacker-controlled query string when certain conditions are met.
The author demonstrates how relaunching navigation from the browser process without binding a renderer source can produce a UXSS (Universal Cross-Site Scripting) primitive by letting Chromium use the current active tab as the implicit source. The post also lists practical challenges to weaponizing the UXSS (for example the requirement that the throttle be fired from specific Microsoft origins) and shows bypass techniques such as using cross-window navigation to bypass origin checks.
Who will find this useful
People who study browser internals, Chromium navigation, or browser security research will get concrete, technical insight into a logic-only exploitation path and the reasoning the author used to chain bugs. Developers and auditors interested in navigation throttles and origin checks may find the concrete failure modes and code-path references helpful for auditing. The content assumes familiarity with browser architecture and security concepts.
Questions people ask about Forging a Microsoft Edge Full Chain with Logic Bugs Only
- Does the post include slides or other presentation material?
- Yes, the author says the bug-hunting and chaining process was shared at HITCON and Hexacon and that slides are available to check.
- Is this exploit based on memory corruption?
- No, the write-up emphasizes the chain is logic-only and does not rely on memory corruption.
- Which specific Edge component was involved?
- The post identifies EdgeCAGuidanceNavigationThrottle, part of Edge’s Conditional Access guidance logic, as a key component involved in the chain.
Forging a Microsoft Edge Full Chain with Logic Bugs Only was shared on NexURLs by Nexis on November 2, 2026, in Scary & Creepy.
What we found on this site
- Served through
- GitHub Pages
- Home page answered in
- 684 ms
- Trackers
- Google Analytics
- Ads
- None found
- RSS feed
- Yes
- Set up for phones
- Yes
- Real-visitor speed
- Passes Core Web Vitals
- Popularity
- Top 200,000 domain (Cloudflare)
- Google safety check
- No threats found
- Domain registered
- 2012
- Domain renews
- November 2032
Checked November 2, 2026 from the site’s own code and public records. See how the rest of the web compares in the NexURLs Internet Report.
Quick answers
What is Forging a Microsoft Edge Full Chain with Logic Bugs Only?
Forging a Microsoft Edge Full Chain with Logic Bugs Only (blog.orange.tw): A detailed write-up of a logic-only exploit chain that achieved a Microsoft Edge sandbox escape at Pwn2Own Berlin 2026. It explains the discovered navigation-throttle bug, how it leads to a UXSS primitive, and the chaining process used to weaponize it.
Who shared Forging a Microsoft Edge Full Chain with Logic Bugs Only on NexURLs?
It was shared by Nexis in November 2026. Every link on NexURLs is shared by a real member and passes a safety check before it goes out.
What are some sites like Forging a Microsoft Edge Full Chain with Logic Bugs Only?
Members found these close to it: Hacking the Eufy Doorbell, Bootable x86 Program Using Just 0s and 1s, Untrusted. The full list is on this page under Sites like Forging a Microsoft Edge Full Chain with Logic Bugs Only.
Sites like Forging a Microsoft Edge Full Chain with Logic Bugs Only
- Hacking the Eufy Doorbelladepts.of0x.cc
This site provides an in-depth analysis of the Eufy Security Doorbell and its ecosystem. It's a valuable resource for...
- Bootable x86 Program Using Just 0s and 1sothmaneblial.github.io
This site offers an interactive simulator for exploring x86 BIOS boot sectors. It's perfect for those interested in...
- Untrustedalexnisnevich.github.io
- Compiler Explorergodbolt.org
Compiler Explorer is an interactive web tool that compiles code and shows the resulting assembly for languages like...
- CSS Battlecssbattle.dev
- Ben Eatereater.net
A site hosting Ben Eater's tutorial-style videos and projects about electronics, computer architecture, networking...
More Scary & Creepy finds
- Dark Tourismdark-tourism.com
- Green Wood Cemeterygreen-wood.com
- Find a Gravefindagrave.com
- Highgate Cemeteryhighgatecemetery.org
- The Horror Treehorrortree.com
- Cemetery Dancecemeterydance.com
Feeling lucky? Try the random website generator.
Where people went next
Nobody has added a next stop yet. Be the first.